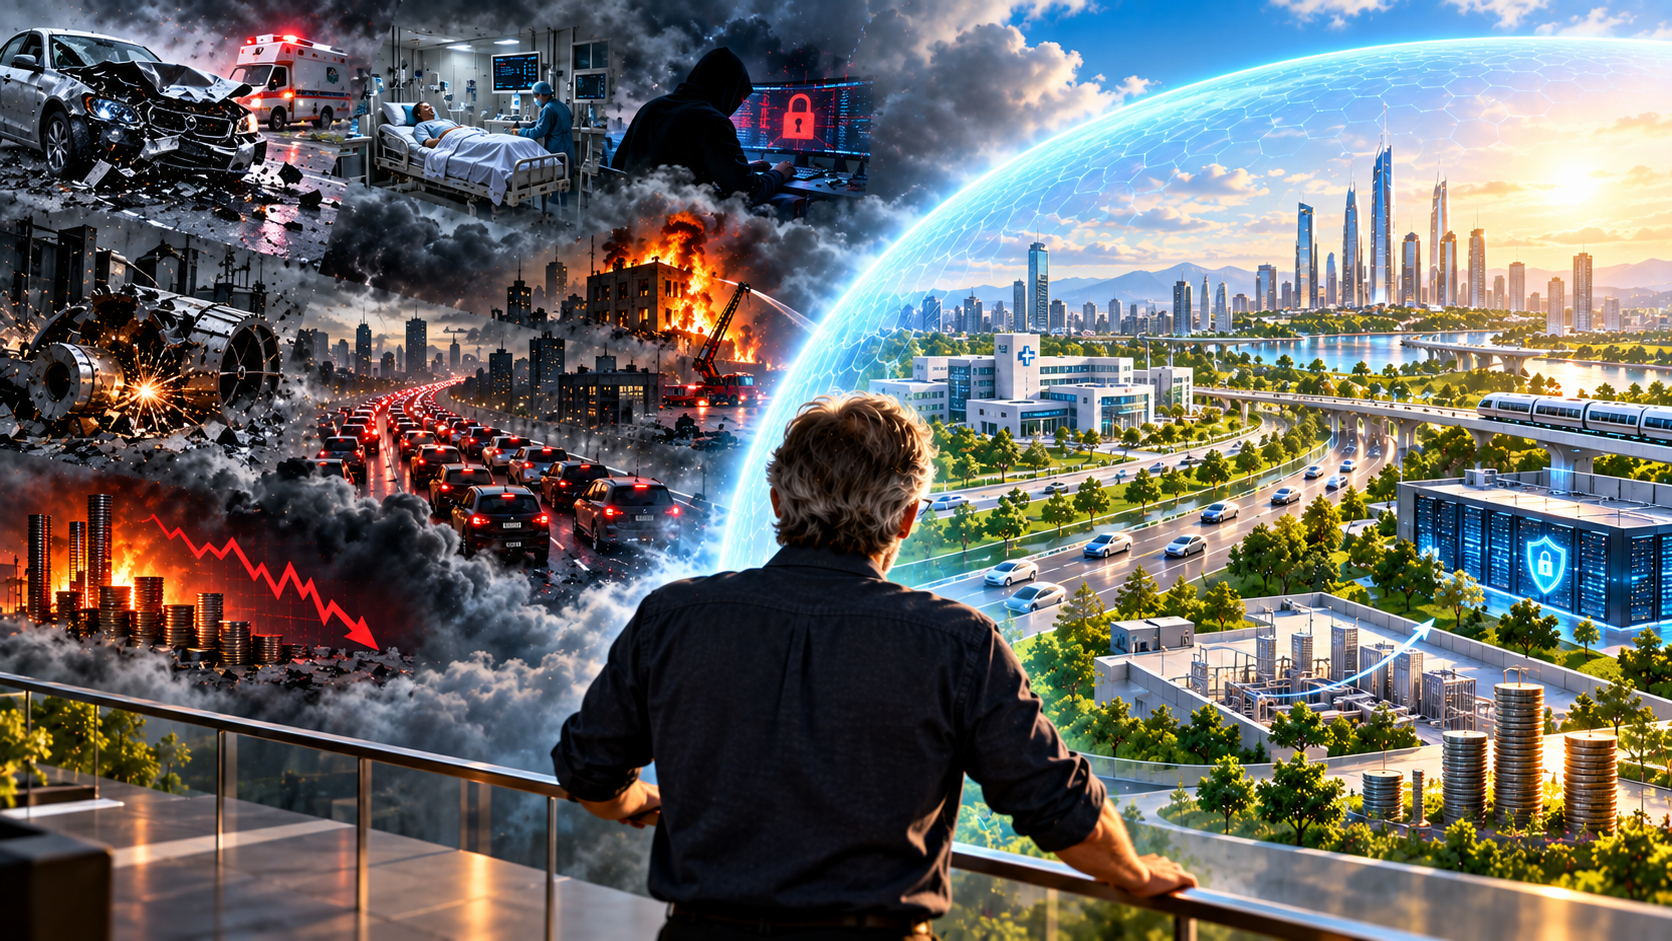
The Economics of Things That Never Happen
How Do You Get Paid for a Disaster No One Ever Saw?
Some of the most valuable technologies of the future will prevent accidents, illnesses, cyberattacks, equipment failures, traffic jams, fires, and financial losses. That creates a fascinating economic problem: how do you measure — and get paid for — an event that technology successfully erased from history?
Imagine two engineers. One spends a career building bridges that stand for a hundred years without incident. The other spends a career responding to bridge collapses, arriving with cranes and rescue teams and headline-making heroics. Which one do you think gets the bigger budget, the louder applause, and the more secure job?
If your gut said the second one, you’ve just identified one of the strangest blind spots in modern economics: we are extraordinarily good at valuing things that happen, and remarkably bad at valuing things that don’t. And as more of our most important technologies shift from reacting to disasters toward quietly preventing them altogether, that blind spot is turning into a genuine economic crisis.
The Invisible Product
Here’s the problem in its purest form. A cybersecurity team spends two million dollars on a new detection system. A year goes by. Nothing happens. No breach, no ransomware, no headline. To the CFO reviewing the budget, that two million dollars looks like pure cost with zero return — because the return, by definition, is an event that never occurred. Security researchers have a name for this exact dilemma: the “prevention paradox.” The primary goal and greatest success of a security program is invisible almost by design, because success looks identical to nothing happening at all.
This isn’t a hypothetical problem confined to corporate IT departments. It’s the same challenge facing hospital systems deciding whether to fund infection-control technology, cities deciding whether to invest in flood barriers, and factories deciding whether a predictive-maintenance sensor is worth the subscription fee. In every one of these cases, the technology’s entire value proposition is a negative: the thing that would have gone wrong, and didn’t.
Contrast that with almost any other kind of investment. A new product line generates five million dollars in traceable revenue. A marketing campaign generates a countable number of leads. Executives love these numbers because they’re tangible, easy to graph, and easy to defend in a budget meeting. Prevention technology offers none of that comfort. Its output is an empty incident log, and empty incident logs don’t make for compelling quarterly reports.
Counting the Disasters That Didn’t Happen
The tool researchers and economists actually use to solve this puzzle is called counterfactual analysis — essentially, building a careful simulation of what would have happened in a world without the intervention, and then measuring the gap between that imagined world and the one we actually got. Disaster-risk researchers describe it as the study of what might have been, used specifically to estimate the losses that were averted by better preparation. It’s how we can honestly say, “This dam prevented roughly $400 million in flood damage,” even though the flood damage in question never actually occurred anywhere except inside a model.
Think about wildfire management as a real-world example. Forest researchers have used counterfactual probabilistic modeling to compare fire-prone landscapes that received fuel treatment against similar landscapes that didn’t, running thousands of simulated fire scenarios across both. The treated landscapes consistently showed reduced fire risk compared to their untreated counterparts — which sounds obvious in principle, but is remarkably hard to prove in practice, because you can’t rerun history twice to see which version burns.
Or consider a more mundane, everyday example that most people have lived through without noticing: predictive maintenance in manufacturing. A sensor on a factory machine picks up a subtle vibration pattern three weeks before a bearing would have failed catastrophically, shutting down an entire production line for two days. The maintenance team swaps the part during a scheduled Tuesday afternoon downtime instead. Nobody claps. No incident report gets filed. The factory just… keeps running, exactly as it was supposed to. The two-day shutdown that didn’t happen is real economic value — it just never shows up anywhere as a line item, because accounting systems aren’t built to record absences.
When Nobody Gets Credit
The counterfactual math is hard enough on its own. But there’s a second problem stacked on top of it: even when you can estimate that something bad was prevented, figuring out who or what deserves the credit is its own tangle.
A recent academic framework analyzing cybersecurity threat-intelligence programs put this precisely: a single prevented attack is rarely the result of one control acting alone. It’s usually a combination of an early warning from a threat-intelligence feed, a firewall blocking a malicious address, detection software terminating a suspicious process, and an employee correctly spotting a phishing email. Untangling which piece of that chain actually gets to claim the win is close to impossible, which means every piece of the chain tends to get underfunded relative to its true contribution, because no one can prove their individual share.
Picture a hospital that goes an entire year without a single central-line infection on a unit that used to average four a year. Was it the new catheter-insertion protocol? The additional nurse training? The redesigned supply cart that made the sterile procedure easier to follow correctly every time? In practice, it’s almost certainly all three working together — but budget conversations rarely reward “all three working together.” They reward the one department that can point to a chart and say, unambiguously, “we did this.”
The Businesses Already Solving This
Here’s the encouraging part: some industries have already built working economic models around exactly this problem, and they offer a blueprint for everyone else.
Insurance is the oldest and most obvious example. An insurer doesn’t wait for your house to burn down to calculate value — it prices risk in advance, using frequency and severity data, and charges a premium today based on disasters that will mostly never occur. That’s a trillion-dollar industry built entirely on monetizing non-events, and it’s worked for centuries.
A newer example is emerging in cybersecurity risk quantification, where researchers have proposed formal breakeven models that convert the probability of an incident, the cost if it happened, and the technology’s mitigation effectiveness into a single number companies can actually budget against — shifting the conversation, as the researchers put it, from “what we prevented” to “how much we reduced our risk.” That reframing matters enormously. You can’t prove a negative, but you absolutely can prove a probability shifted, and probabilities are something budget committees know how to fund.
My Prediction: Prevention-as-a-Service
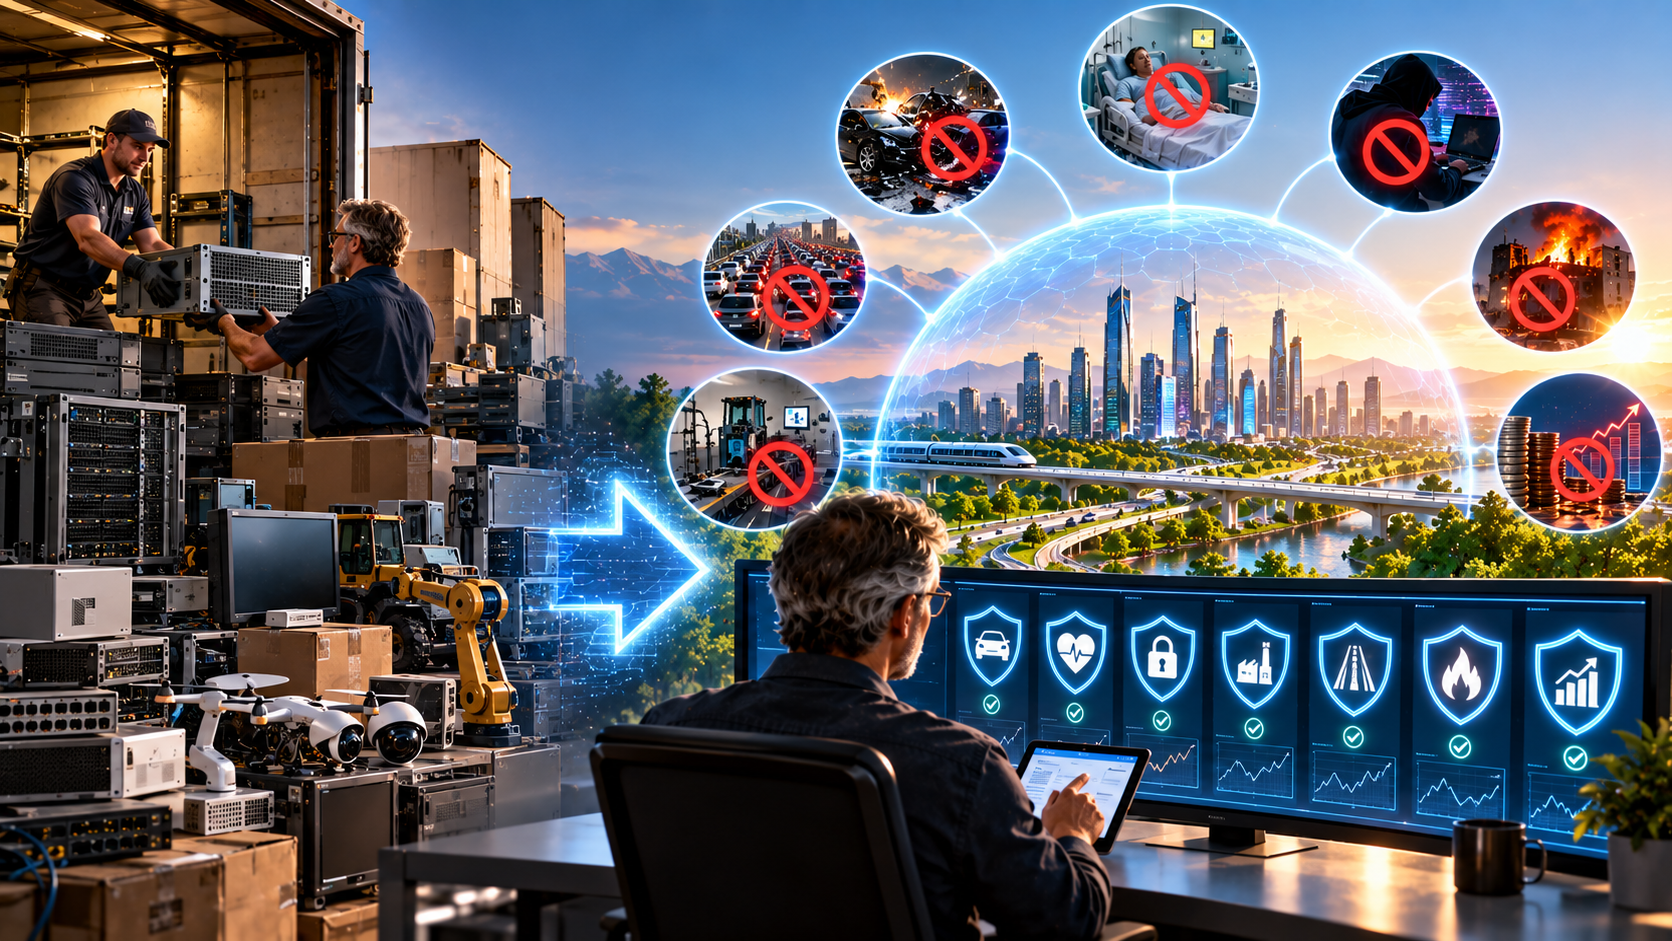
I believe the next major shift in how we pay for technology will be a move away from buying tools and toward buying guaranteed non-events — literally subscribing to an outcome rather than a device.
Picture a highway system that pays an AI traffic-management company not for the software license, but for every hour of gridlock that didn’t happen, measured against a modeled baseline of what traffic would have looked like without it. Picture a hospital that pays its infection-prevention vendor a bonus tied directly to infections that didn’t occur, benchmarked against its own historical average. Picture an insurance company that reduces your premium in real time, month by month, based on a continuously updated model of the disasters your smart-home sensors are actively preventing before they’d ever reach a claims adjuster’s desk.
This kind of “prevention-as-a-service” pricing already exists in fragments — performance-based cybersecurity contracts, pay-for-outcomes healthcare programs, insurance telematics that reward safe driving in real time. What’s missing is the standardized measurement infrastructure to make it work at scale everywhere at once: agreed-upon baselines, agreed-upon counterfactual models, and agreed-upon ways to split credit across the many tools working together behind any single non-event.
The company or city that solves this measurement problem first won’t just save money — it will unlock enormous pools of capital currently sitting on the sidelines because investors can’t yet put a confident number on the value of things that never happen. Once someone builds a genuinely trustworthy meter for measuring absence, prevention stops being an unrewarded cost center and starts being one of the most valuable, fundable categories in the entire economy.
The future doesn’t just belong to the technologies that fix our problems. It belongs to the ones clever enough to prove, with real numbers, that the problem never had to happen at all.
Related Articles
- “Measuring Cybersecurity ROI: A Framework For 2026 Decision-Makers” — Safe Security — safe.security/resources/blog/measuring-cybersecurity-roi-a-framework-for-2026-decision-makers
- “Resetting the Economics of Prevention: How CIOs Can Deliver Reliability and Possibility” — CIO — cio.com/article/4143003/resetting-the-economics-of-prevention-how-cios-can-deliver-reliability-and-possibility.html
- “Assessing the ROI of Cyber Threat Intelligence: An Operational and Financial Evaluation Framework” — arXiv (Strada & Cimato, University of Milan) — arxiv.org/pdf/2507.17628